Cybercriminals don’t need to break down your digital walls with sophisticated hacking tools. They simply send an email that looks legitimate, wait for an unsuspecting employee to click a link, and watch as your entire network is compromised. Phishing training is the single most effective defense against this threat, yet many New York nonprofits treat it as an afterthought—or skip it entirely. The result is devastating: ransomware attacks, data breaches, stolen donor information, and reputational damage that can take years to repair. At Iconyx Technology, we have seen firsthand how phishing training transforms nonprofit security. We have also seen the consequences when phishing training is inadequate or missing. This comprehensive guide exposes five crippling phishing training failures that destroy nonprofits and shows you exactly how to avoid them.
Whether you are a small community center with a handful of staff or a statewide nonprofit with hundreds of employees and volunteers, phishing training is not optional. It is a critical component of your cybersecurity strategy. Phishing training empowers your team to recognize and report suspicious emails, turning your staff from your weakest link into your strongest defense. Phishing training also supports compliance with New York’s SHIELD Act and other regulations that require reasonable safeguards for private information. With Iconyx Technology as your partner, your phishing training program can become a cornerstone of your security posture rather than a checkbox exercise.
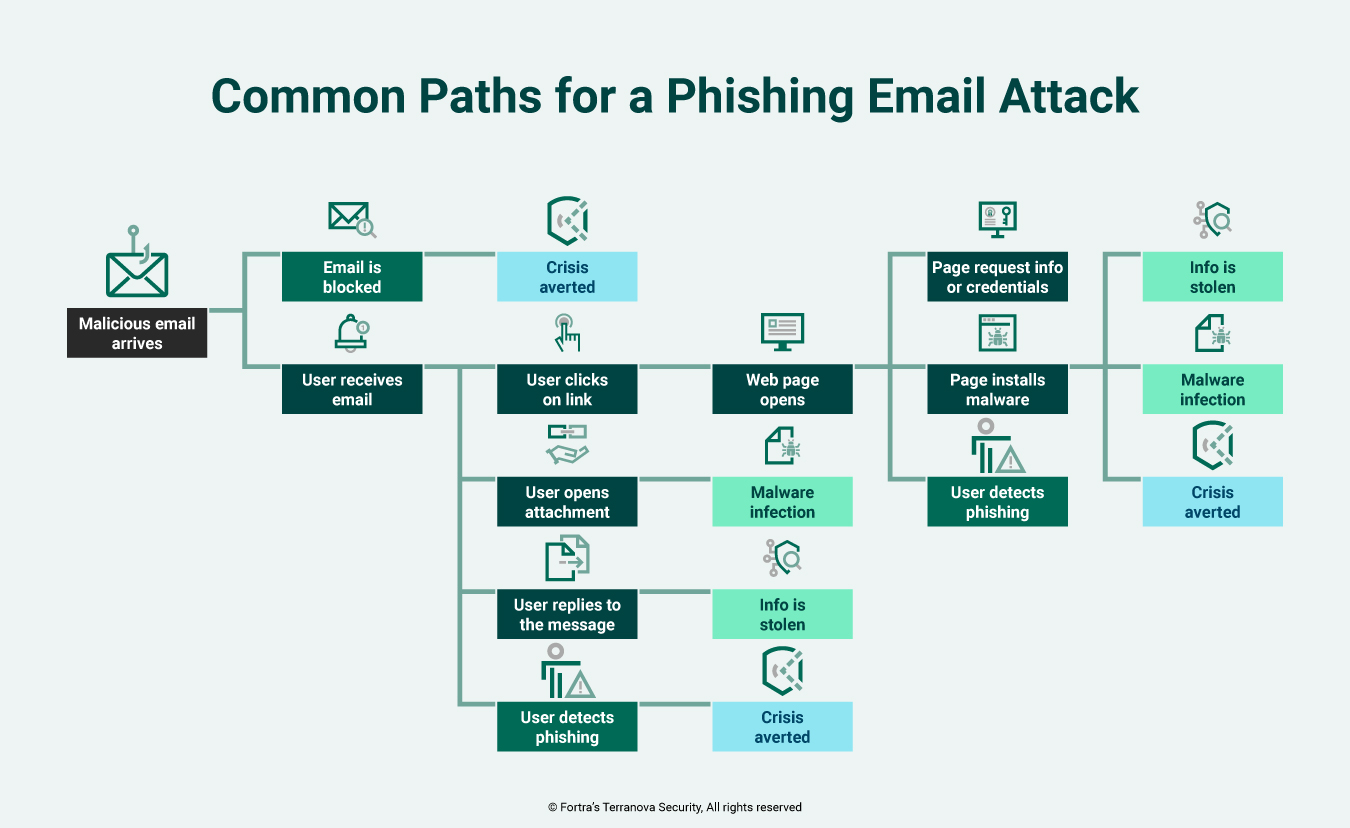
Phishing training is the process of educating employees, volunteers, and contractors about phishing attacks—fraudulent emails designed to trick recipients into revealing sensitive information, clicking malicious links, or downloading malware. Effective phishing training teaches staff how to recognize the signs of a phishing email, how to verify suspicious requests, and how to report potential threats. Phishing training often includes simulated phishing exercises that test employees’ ability to identify and respond to fake attacks, providing measurable data on your organization’s security awareness.
Phishing training matters for nonprofits because phishing is the leading cause of data breaches and ransomware attacks. Cybercriminals target nonprofits because they often lack enterprise-grade security and because their data—donor financial information, client records, health data—is valuable. A single successful phishing attack can compromise your entire network, exposing sensitive information and triggering regulatory penalties. Phishing training is the most cost-effective way to reduce this risk. It is far cheaper to train your staff than to recover from a breach. Understanding phishing training deeply—and implementing it effectively—is one of the most responsible decisions a nonprofit can make.
The most devastating phishing training failure is treating it as a one-time event. Many nonprofits conduct phishing training during onboarding, check the box, and never revisit the topic. This approach is dangerously inadequate. Phishing tactics evolve constantly. Cybercriminals develop new techniques, new lures, and new technologies. What employees learned six months ago may not protect them against today’s threats. Without ongoing phishing training, your staff become complacent, and your organization becomes vulnerable.
Effective phishing training must be ongoing. It should include regular refreshers—at least quarterly—that update staff on new threats and reinforce key concepts. Phishing training should also include simulated phishing exercises that test employees’ vigilance and provide opportunities for learning. Iconyx Technology delivers phishing training that is continuous, engaging, and effective. We provide regular training modules, simulated phishing campaigns, and real-time feedback that keep phishing training top of mind. Our phishing training approach ensures that your staff remain vigilant year-round, not just during onboarding.
A second crippling phishing training failure is delivering generic, boring content that fails to engage employees. Many phishing training programs consist of lengthy videos, dense policy documents, and multiple-choice quizzes that employees click through as fast as possible. This type of phishing training accomplishes nothing. Employees don’t retain the information, and they don’t change their behavior. In fact, boring phishing training can breed resentment and resistance.
Effective phishing training must be engaging, relevant, and tailored to your organization. It should use real-world examples that employees can relate to—emails that look like they could land in their actual inboxes. Phishing training should include interactive elements, scenarios, and immediate feedback. It should also be role-specific, recognizing that a finance officer faces different risks than a volunteer coordinator. Iconyx Technology creates phishing training that is customized for nonprofit environments. We use realistic scenarios, engaging formats, and role-specific content that resonates with your staff. Our phishing training doesn’t just check a box—it changes behavior.
A third devastating phishing training failure is failing to measure effectiveness. Many nonprofits conduct phishing training but have no idea whether it is working. They don’t track click rates, report rates, or improvement over time. Without measurement, you cannot know if your phishing training is reducing risk or if it needs improvement. You are flying blind.
Effective phishing training includes robust measurement. Simulated phishing campaigns provide data on how many employees click, how many report, and how these metrics change over time. Phishing training platforms track completion rates, quiz scores, and engagement. This data allows you to identify high-risk departments, tailor additional phishing training, and demonstrate improvement to leadership and funders. Iconyx Technology’s phishing training includes detailed analytics and reporting. We provide you with clear metrics on your organization’s phishing resilience. Our phishing training doesn’t just teach—it proves its value through measurable results.
A fourth crippling phishing-training failure is focusing only on full-time employees while ignoring volunteers, contractors, and remote workers. Many nonprofits rely heavily on volunteers who have access to email, databases, and internal systems. Remote workers connect from home networks and personal devices. If these groups don’t receive phishing-training, they become easy targets for cybercriminals. A single untrained volunteer can click a malicious link and compromise your entire network.
Effective phishing-training must extend to everyone with access to your systems—employees, volunteers, contractors, and remote workers. Phishing-training should be mandatory for all, regardless of their role or location. Iconyx Technology delivers phishing-training that reaches your entire workforce. We provide scalable phishing-training solutions that work for volunteers who may only engage occasionally and for remote workers who need training from anywhere. Our phishing-training ensures that no one is left unprotected.
A fifth devastating phishing-training failure is treating phishing-training as a standalone solution rather than integrating it with technical controls. Phishing-training is essential, but it is not enough on its own. You also need email filtering, endpoint protection, multi-factor authentication, and other technical safeguards that catch what training misses. When phishing-training is integrated with technical controls, you create a layered defense that dramatically reduces risk.
The solution is to integrate phishing-training with your broader cybersecurity strategy. Use email filtering to block many phishing messages before they reach inboxes. Implement multi-factor authentication to prevent credential theft even if a phishing link is clicked. Deploy endpoint protection to detect and block malware. Then layer phishing-training on top to empower your staff to be the first line of defense. Iconyx Technology provides phishing-training as part of a comprehensive cybersecurity program. We ensure that your phishing-training is complemented by technical controls that protect your organization. Our integrated approach maximizes security while minimizing risk.
Beyond preventing breaches, effective phishing-training aligns with several core needs unique to nonprofits operating in New York. First, phishing-training compliance is a legal requirement. New York’s SHIELD Act mandates reasonable safeguards for private information, and phishing-training is a recognized best practice. Phishing-training helps you meet your regulatory obligations while protecting your data.
Second, phishing-training builds donor trust. Donors want to know that their financial information is protected. When you demonstrate a commitment to phishing-training and cybersecurity, you reassure donors that their contributions are safe. This trust translates into continued giving and stronger relationships.
Third, phishing-training supports grant compliance. Many grant agreements require specific data security measures, including phishing-training for staff. Robust phishing-training documentation demonstrates to funders that you meet their requirements, strengthening your grant applications and compliance reporting. Iconyx Technology helps nonprofits articulate their phishing-training efforts in language funders appreciate, providing documentation and assessments that support funding requests.
Not all phishing-training programs are identical. When evaluating phishing-training for your nonprofit, look for these essential features:
Ongoing training modules delivered regularly, not just at onboarding.
Simulated phishing campaigns that test real-world vigilance.
Role-specific content tailored to different job functions.
Engaging, interactive formats that capture attention.
Real-time feedback when employees click or report simulated phish.
Measurable analytics tracking click rates, report rates, and improvement.
Scalability for employees, volunteers, contractors, and remote workers.
Integration with technical controls like email filtering and MFA.
Compliance documentation for SHIELD Act, HIPAA, and grant requirements.
Local support from a provider who understands New York nonprofits.
Iconyx Technology preconfigures each phishing-training engagement with these features, tailoring the program to your organization’s specific needs. We don’t just deliver training and walk away; we become your security partner, invested in your resilience.
The thought of implementing a comprehensive phishing-training program can feel daunting, but the process is more manageable than most nonprofits anticipate. A professional partner like Iconyx Technology begins with a baseline assessment. We conduct a simulated phishing campaign to measure your current susceptibility. We then design a phishing-training program tailored to your results and your organization’s culture. We deliver training modules, run ongoing simulations, and provide regular reports. Within weeks, your organization’s phishing resilience improves measurably.
Because phishing-training is delivered online and can be completed in short sessions, staff experience minimal disruption. They can complete training at their convenience, from any device. Iconyx Technology provides ongoing support and optimization, ensuring that your phishing-training continues to evolve as threats change.
Let’s examine a realistic scenario for a mid-sized New York nonprofit with 30 staff members. A comprehensive phishing-training program—including baseline assessment, ongoing modules, simulated campaigns, and reporting—might cost $2,000–$5,000 annually. A single successful phishing attack, by contrast, can cost far more: ransomware payments averaging tens of thousands of dollars, downtime lasting weeks, lost donor confidence, legal fees, and regulatory penalties. The average cost of a data breach for a small organization exceeds $100,000. Phishing-training is not an expense—it’s insurance against catastrophe. Iconyx Technology provides detailed cost-benefit analyses for every phishing-training engagement, showing you exactly how the investment protects your organization.
Q: How often should we conduct phishing-training?
A: Phishing-training should be ongoing, with refreshers at least quarterly and simulated phishing campaigns monthly or quarterly.
Q: Who needs phishing-training?
A: Everyone with access to your systems—employees, volunteers, contractors, and remote workers—should receive phishing-training.
Q: How do we measure phishing-training effectiveness?
A: Track click rates, report rates, and improvement over time through simulated phishing campaigns. Iconyx Technology provides detailed phishing-training analytics.
Q: Can phishing-training be delivered remotely?
A: Yes. Phishing-training is typically delivered online and can be completed from any device, making it ideal for remote and distributed teams.
Q: How does phishing-training support compliance?
A: Phishing-training is a recognized best practice for SHIELD Act, HIPAA, and other regulations. Documentation of phishing-training supports compliance reporting.
We are not just a generic training provider. Iconyx Technology is a New York-based IT and VoIP firm that has spent years serving the local nonprofit community. We understand the funding constraints, the compliance landscape, and the operational rhythms of mission-driven organizations. When you choose phishing-training from us, you get a program architected for the way you work: engaging, measurable, and mission-focused. Our phishing-training is backed by local support, responsive service, and a genuine commitment to your success that goes beyond the contract. We will be your phishing-training advisor, not just a vendor, and we will stand with you as threats evolve.
Your staff shouldn’t be your weakest link. Those five crippling phishing-training failures—one-time training, boring content, no measurement, ignoring volunteers and remote workers, and missing technical integration—are all avoidable with the right phishing-training program. Imagine a future where your team recognizes phishing emails instantly, reports them proactively, and protects your organization from attack. That future is what effective phishing-training delivers, and it’s available right now through Iconyx Technology.
Don’t let another quarter go by with inadequate phishing-training that leaves your nonprofit exposed. Contact Iconyx Technology today for a free consultation and a personalized phishing-training assessment designed specifically for New York nonprofits. Let’s walk through your current risks, identify vulnerabilities, and design a phishing-training program that protects your mission, your data, and the people who trust you. The shift to professional phishing-training is simpler, faster, and more transformative than you ever imagined—and your nonprofit deserves nothing less.